150+
AI Code Audits Completed
60+
Software Products Evaluated
12+
Years of Code Review Experience
40+
Industries Supported Globally
AI Code Audit Services Aligned With Software Quality Goals
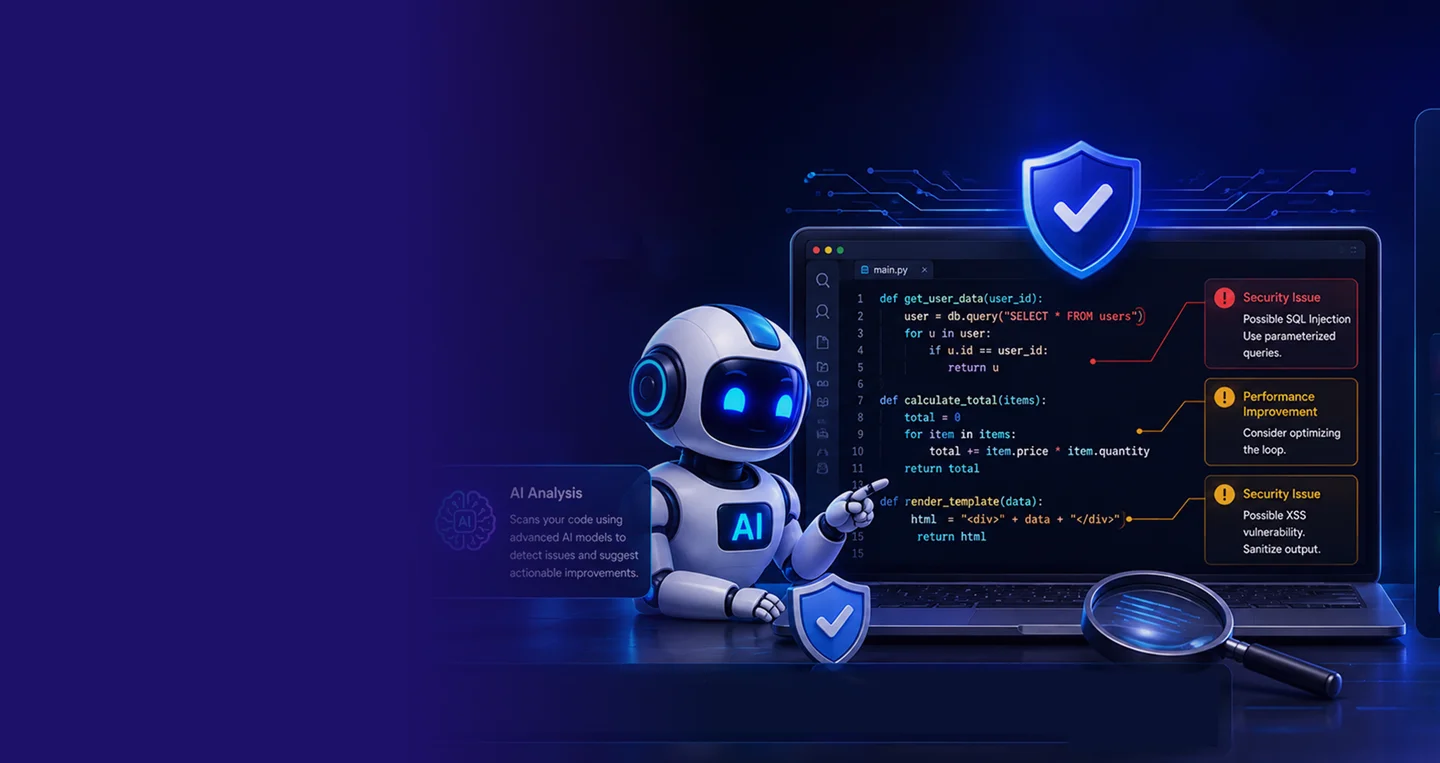
We combine AI-assisted code analysis with experienced engineering review to identify technical issues, assess potential risks, and uncover improvement opportunities that automated tools alone may miss.
Identify Why Your Business Needs an AI Code Audit
Review AI-generated and existing code to uncover security vulnerabilities, quality issues, and technical gaps before they affect application reliability, performance, or business operations.
Security Gaps in AI-Generated Code
AI can produce functional code quickly, but functionality does not always mean security. Without proper review, AI-generated code may introduce weaknesses such as injection risks, poor authentication logic, insecure inputs, and unsafe configurations.
Unverified Dependency Exposure
AI coding tools can recommend incorrect, outdated, or unreliable libraries. Using unverified dependencies may introduce malicious packages, compatibility issues, and security risks that become difficult to detect after they enter the codebase.
Growing Technical Complexity
AI-generated code can solve individual development tasks without considering the wider application architecture. Over time, this can create duplicated logic, inconsistent patterns, and technical issues that affect scalability and long-term maintenance.
Compliance and Governance Concerns
Businesses operating under security and compliance requirements need visibility into how their software is developed and reviewed. An AI code audit helps establish human oversight, documentation, and validation practices for AI-assisted development.
Greater Focus on Technical Due Diligence
A codebase is an important part of technical due diligence for investors, partners, and potential buyers. Regular code audits help demonstrate that security, quality, and engineering risks are actively reviewed and managed.
Unmonitored AI Usage Across Teams
Developers may adopt AI coding tools without consistent internal guidelines or review processes. An AI code audit helps businesses identify where AI generated code is being used and ensure it meets established quality and security standards.
A Structured Approach to the iTechnolabs AI Code Audit Process
At iTechnolabs, we follow a structured five-step audit process to assess your codebase, prioritize critical risks, and deliver clear recommendations that support software quality, security, and maintainability.
Get a Clear View of Your Codebase Risks
Start Your AI Code Audit Consultation
Tell us about your requirements, and our specialists will connect with you within 24 hours
AI Code Audits Aligned With Industry Requirements
Different industries operate under different security, compliance, and operational requirements. We tailor each AI code audit to your business context, identifying code issues that could affect data protection, application performance, compliance obligations, and user trust.
Enterprise AI Platforms
AI-powered enterprise applications often combine models, APIs, databases, automation workflows, and third-party systems. Our audit evaluates these connected components to identify code quality, security, integration, and performance concerns across the wider application environment.
Why Businesses Choose iTechnolabs for AI Code Audits
We combine software engineering expertise, AI-assisted assessment, security-focused practices, and practical development knowledge to evaluate your codebase and provide actionable recommendations for improvement.
Technologies Assessed Through Our AI Code Audits
We evaluate applications built with modern technologies to identify security vulnerabilities, code quality issues, performance constraints, and maintainability concerns that may affect software reliability and future development.
Get Your AI Code Audit Started
Tell us about your requirements, and our specialists will connect with you within 24 hours
Build software you can trust with a thorough AI Code Audit.
Our experts review your code to uncover security vulnerabilities, quality concerns, and technical risks that could affect performance and scalability. Get clear, actionable recommendations to strengthen your codebase before issues reach production.
Frequently Asked Questions
What is an AI Code Audit?
An AI Code Audit is a structured assessment of AI-generated and existing application code. It examines security vulnerabilities, code quality, dependencies, performance, and architecture. By combining automated analysis with expert engineering review, an audit helps identify technical risks and provides recommendations to improve software reliability and production readiness.
Can you audit code written using AI coding tools?
Yes. An AI Code Audit can assess code produced with AI coding assistants as well as code written by developers. The review examines implementation quality, application logic, dependencies, and security controls. AI-generated code still requires independent validation because generated output can contain errors that are not immediately obvious.
What security risks can AI-generated code introduce?
AI-generated code may contain missing authorization checks, weak input validation, insecure dependencies, exposed credentials, and incorrect business logic. These issues can create vulnerabilities even when the application appears to work correctly. A structured code review helps identify potential weaknesses before they become production problems.
What does an AI Code Audit examine?
An AI Code Audit can examine source code quality, application architecture, business logic, third-party dependencies, security controls, and performance concerns. The assessment may also review relevant databases, AI frameworks, and deployment technologies. The exact scope depends on the application's complexity, technology stack, and audit requirements.
Can you audit an existing application before it goes live?
Yes. An existing application can be reviewed before production deployment to identify security gaps, architectural weaknesses, dependency risks, and code quality concerns. An audit is also useful after major development changes or when introducing AI-generated code into an established application.
Is an AI Code Audit the same as penetration testing?
No. An AI Code Audit focuses on examining source code, implementation quality, architecture, and potential vulnerabilities. Penetration testing evaluates an application by testing its security from an attacker's perspective. Both can contribute to application security, but they address different areas and should be scoped according to the project's requirements.
What do we receive after an AI Code Audit?
The audit provides findings on identified code, security, performance, and architectural concerns, along with practical recommendations for improvement. Findings should be prioritized according to their severity and potential impact so development teams can understand which issues need attention first. The review scope determines the level of detail provided.
Can iTechnolabs help validate issues after the audit?
Yes. Code quality and security need attention beyond the initial assessment. Follow-up review and validation can help determine whether identified issues have been addressed and whether changes introduce new concerns. The specific remediation and validation activities should be agreed upon as part of the audit scope.
How much does an AI Code Audit cost?
An AI Code Audit at iTechnolabs typically costs between $2,000 and $10,000. The final estimate depends on codebase size, application complexity, technology stack, number of systems, and review depth. Larger enterprise applications or ongoing assessment requirements may need a separately defined scope and estimate.
How long does an AI Code Audit take?
A standard AI Code Audit typically takes 1 to 3 weeks. A smaller application or focused review may take around 5 to 7 business days, while larger or more complex codebases can require 3 to 6 weeks. The timeline depends on audit scope, code volume, and technical complexity.